How We Handle Customer Data

At Tuklas, your data is yours. We built our platform around a simple idea: no one should see your data unless you say so — not even us, beyond what is needed to run the service.
This post explains, in plain words, how we keep your data safe, what you can control, and the options available for organizations and users who need extra protection.
The Short Version
- Everything you send to Tuklas is encrypted while traveling (in transit) and while sitting in our database (at rest).
- Sensitive fields inside your records are encrypted with your own keys, not just ours.
- Organizations cannot read user data unless the user signs a consent.
- Enterprise clients and high-risk users can bring their own keys (BYOK) for the strongest privacy.
- You can reach us anytime at [email protected].
How Tuklas Protects Data — The Three Levels
We offer three levels of data protection. Levels 1 and 2 are default for everyone — you don't have to do anything. Level 3 is an opt-in for enterprises and high-risk users.
Level 1 — Basic (default for everyone)
This is what every user and organization gets the moment they sign up. No setup, no extra cost.
What we do:
- In transit: All data sent between your device and Tuklas is encrypted using TLS (the same standard banks use).
- At rest: All data stored on our servers is encrypted using AES.
- Identity keys: When you register, Tuklas automatically creates a cryptographic key pair for you. This key is your digital identity on the platform.
- Signed actions: Every important action (granting consent, joining a group, signing a document) is cryptographically signed by your key — so no one can fake it later.
From the user's point of view:
You just log in with Google or Apple. Tuklas takes care of everything else. Your key is made for you, kept safe for you, and used on your behalf when you approve actions.
From the organization's point of view:
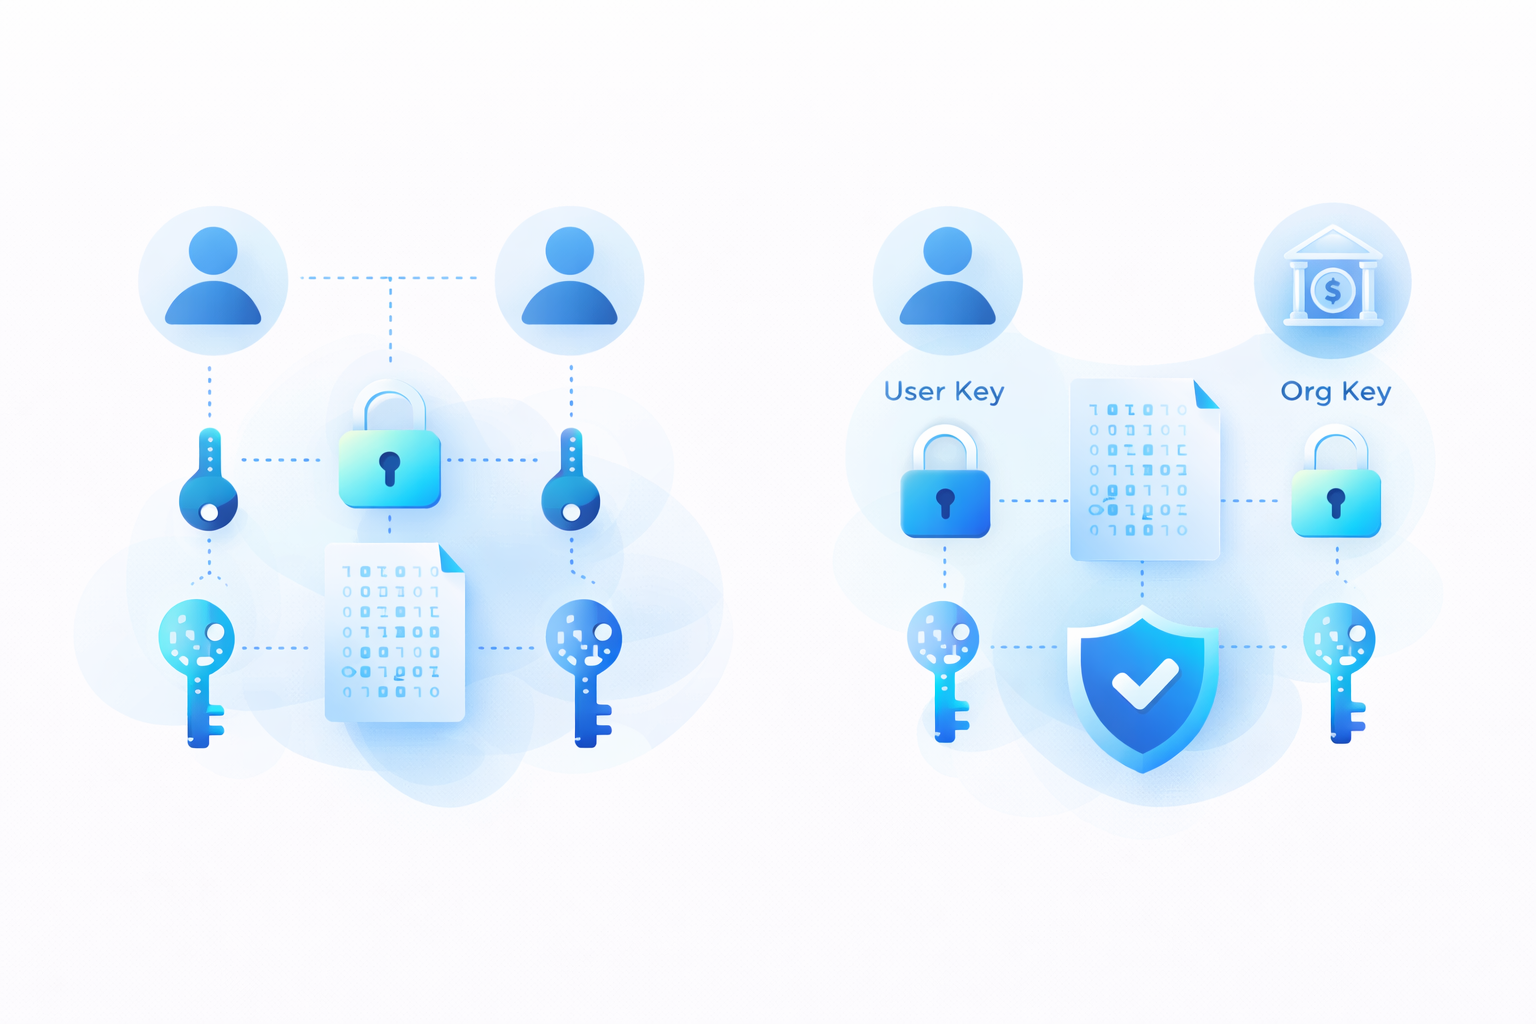
Your organization also gets its own key. Member data inside the org is locked with the org key. Only members with a valid grant (a signed permission slip) can read it.
Who this is for: Most users and most organizations. This is already a very strong baseline.
Level 2 — Enhanced (consent-based sharing + field-level encryption)
Level 2 is also default for everyone — you do not have to ask for it or turn it on. It kicks in the moment organizations try to share data with each other, or when you join a group. No extra setup, no extra cost.
What we do:
- Consent grants: Organizations cannot pull your data just because you joined. They must ask, and you must sign a consent. The consent says which fields, for how long, and for what purpose. If you say no, they get nothing.
- Grants are cryptographic, not a lookup table. A grant is not a row in a database that says "Org A is allowed to see User B's data." That kind of list can be flipped, faked, or quietly edited by anyone with database access. Instead, a Tuklas grant is a signed, encrypted document. It carries the actual key needed to unlock your data inside it — locked with the recipient organization's public key, and signed by your private key. If the grant is tampered with, the signature breaks and the grant becomes useless. If the grant doesn't exist, there is no key anywhere in the system that can open your data for that org — not even ours. This is the difference between a permission claim and a permission proof.
- Field-level encryption: Sensitive fields (like ID numbers, health info, phone, address) can be encrypted individually — not just the whole record. Even if someone got access to the database, they'd still see gibberish without the right key.
- Organization isolation: Your data inside Organization A is encrypted with A's keys. Organization B cannot read it — period. No "accidental" sharing.
From the user's point of view:
You always see what each organization is asking for and can revoke access anytime. No surprises.
From the organization's point of view:
You can prove to your clients and auditors that you never touched data without a signed, tamper-proof consent. Every access is logged in a chain that can be verified from end to end.
Level 3 — Custom Key Custody (BYOK — Bring Your Own Keys)
This is the highest level. It is for enterprises and high-risk individuals who need maximum control.
What it means:
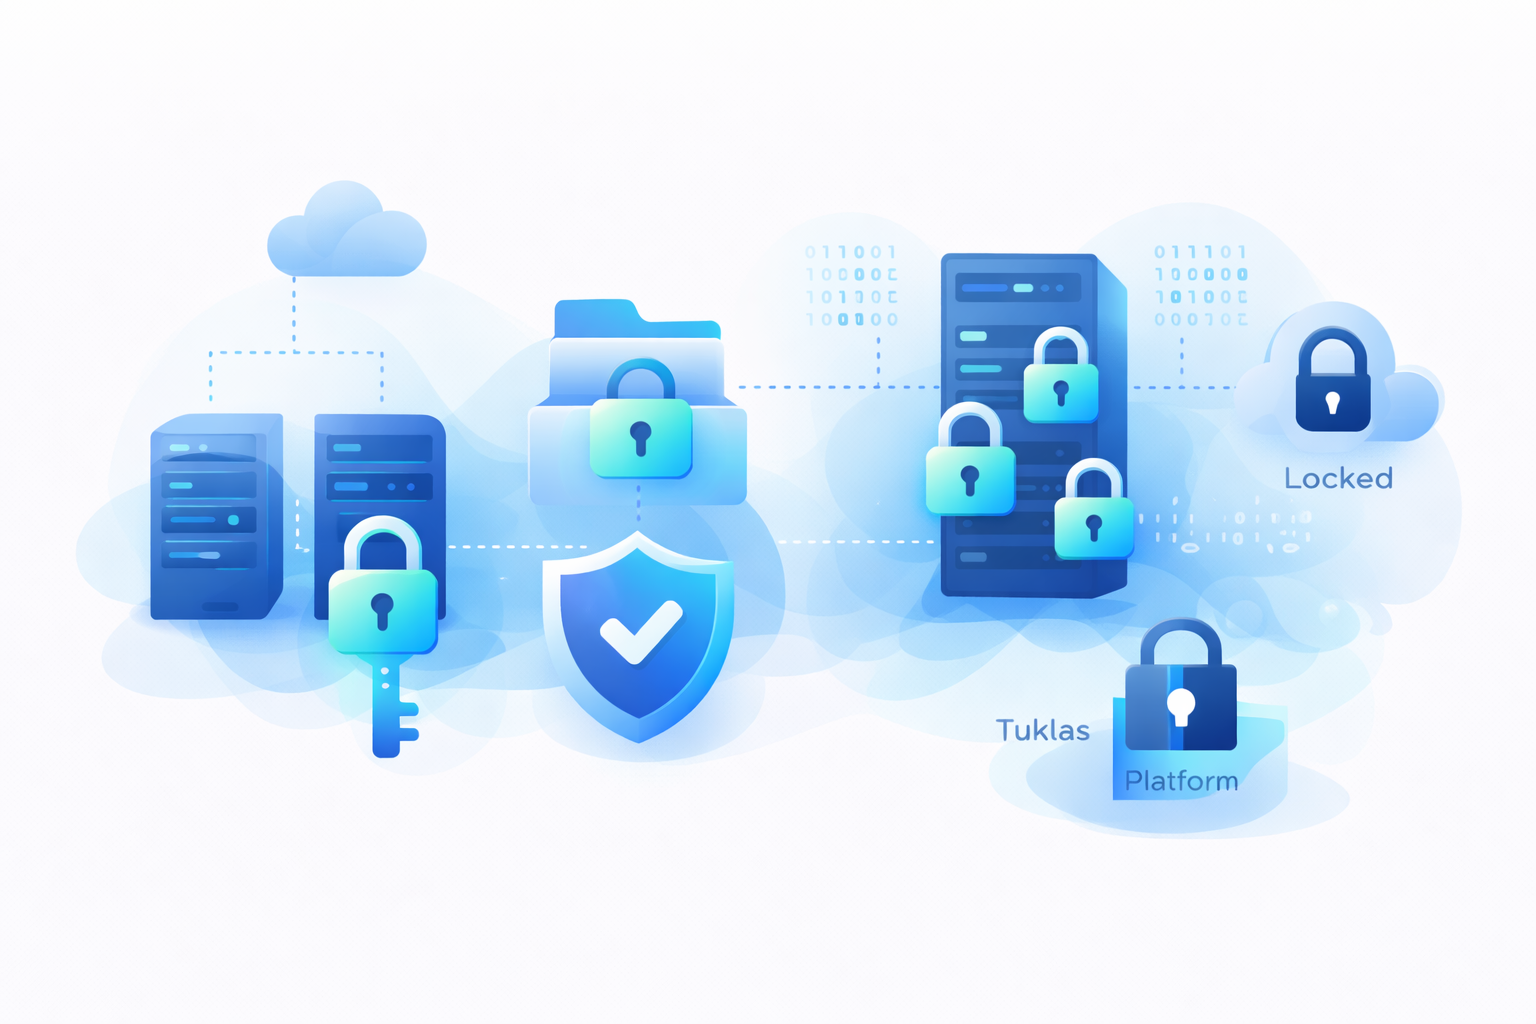
Instead of Tuklas managing your keys for you, you run your own Key Management System (KMS). Your data is still stored on our platform, but the keys that unlock it live on your side. Not ours.
If someone ever tried to compel Tuklas to hand over your data — by any means — we literally could not read it. We don't have the key.
Who is this for?
- Government officials and public servants who handle sensitive matters.
- Enterprise organizations with strict compliance requirements (health, finance, legal).
- Journalists, activists, or private individuals in sensitive positions who need the highest confidentiality.
The pros:
- Maximum privacy. Even Tuklas staff cannot read your data.
- Full control. You decide who can access what, from your own system.
- Regulatory peace of mind. Easier to meet strict compliance rules (data sovereignty, audit, legal holds).
- Strong defense against legal or third-party requests. Tuklas cannot produce data we cannot decrypt.
The cons (please read carefully):
- You are responsible for your keys. If you lose your keys, your data is gone. We cannot recover it. There is no "forgot password" for cryptographic keys.
- You need the people and tools to manage a KMS. A KMS needs backups, rotation policies, access controls, and a plan for key loss. This is a real operational commitment.
- Higher cost. BYOK is available on enterprise plans.
- Some features may work differently. A few platform features (like cross-org analytics) depend on keys Tuklas manages; with BYOK, those may need special configuration or be limited.
The waiver:
Because data loss from a lost key is permanent, we ask BYOK clients to sign a waiver form before onboarding. The waiver confirms two things:
- You understand that if your keys are lost, your data cannot be recovered — not by us, not by anyone.
- You have the capability (people, tooling, processes) to run your own KMS safely.
This isn't fine print to scare you. It's to make sure you go in with eyes open.
How to get it: Email [email protected]. We'll walk you through the onboarding.
A Quick Recap
| Level | Who it's for | What you do |
|---|---|---|
| Basic | Everyone (default) | Nothing — it's automatic |
| Enhanced | Everyone (default) | Just approve or deny consents when asked |
| Custom (BYOK) | Enterprises, gov officials, high-risk users | Contact us, sign waiver, run your own KMS |
No matter which level you use, these stay the same:
- Your data is always encrypted in transit and at rest.
- Your actions are always signed so they can be verified later.
- Organizations never access your data without your consent.
- You can leave and take your data with you.
Questions?
We welcome them. Privacy is not a checkbox for us — it is the foundation of Tuklas.
Email: [email protected]
We'll reply personally. If you are a government official, enterprise admin, or exploring BYOK, mention it in your email and we'll route you to the right team.